


Every pull request, reviewed before it merges
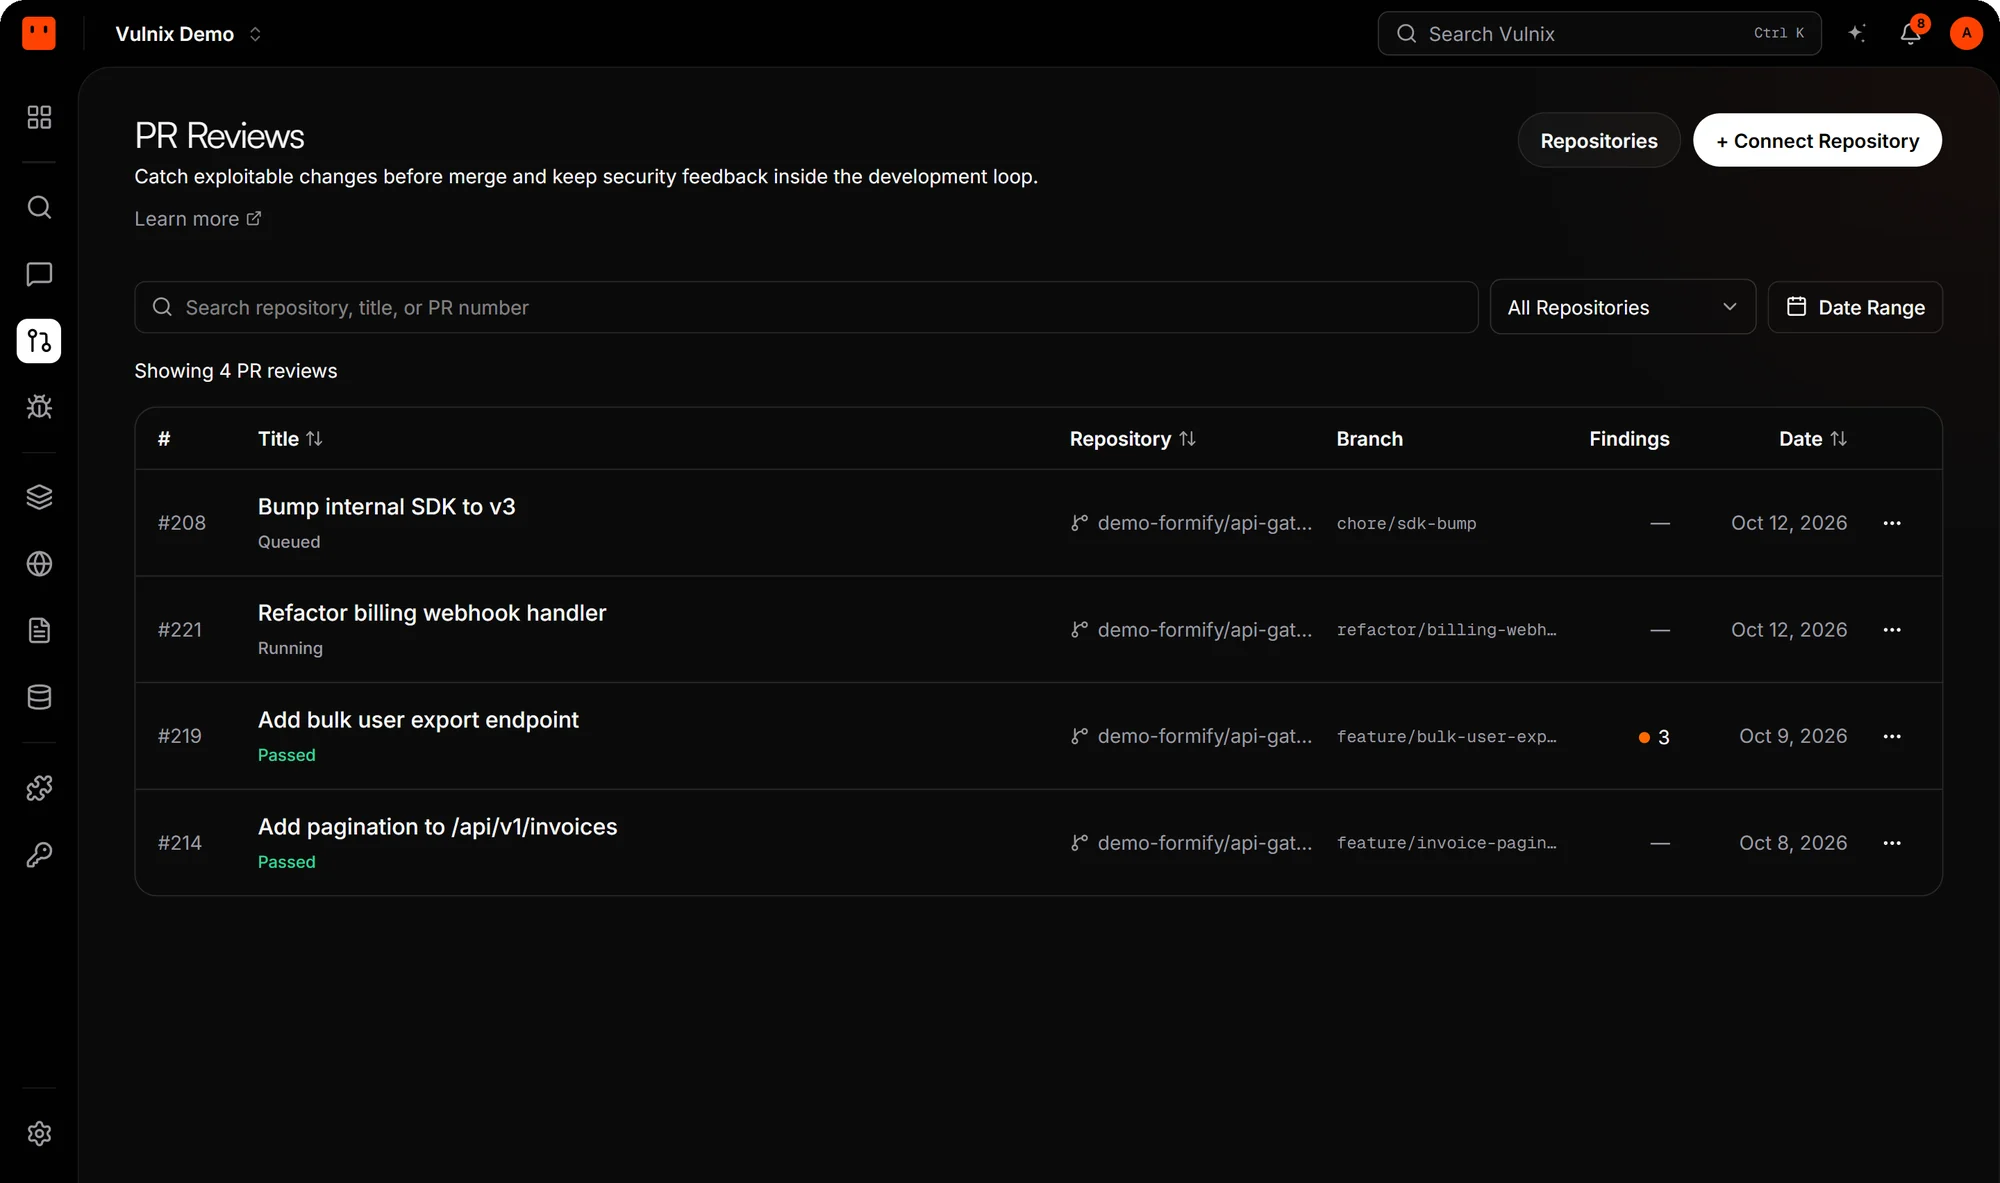
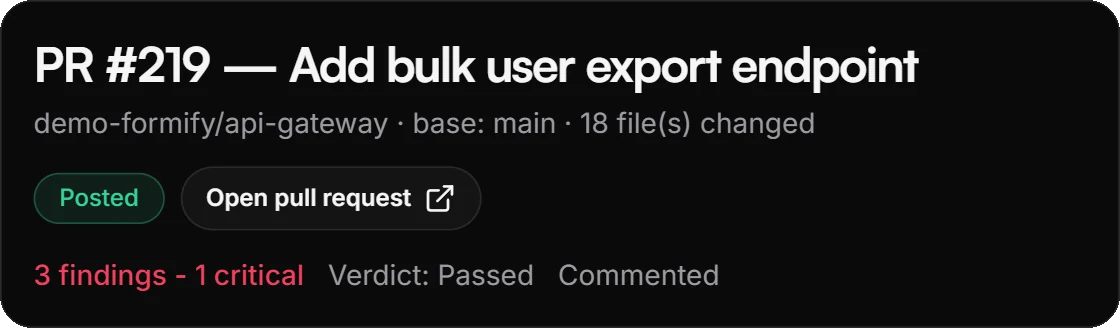
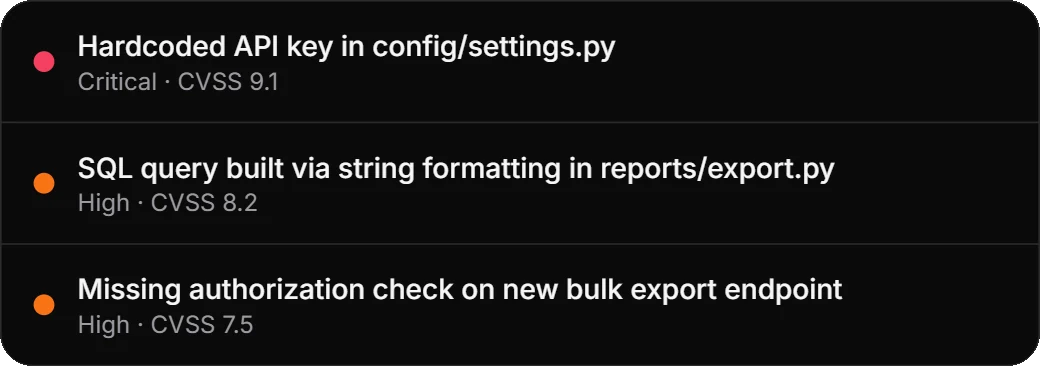
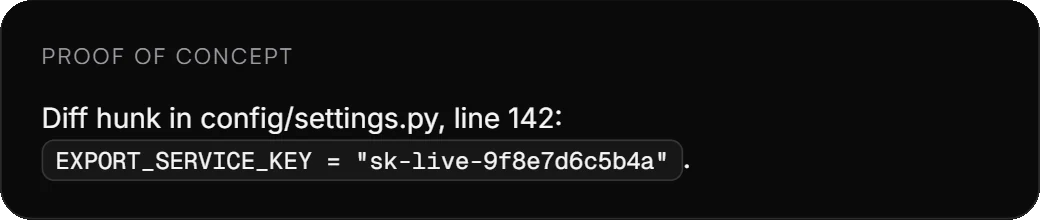
Vulnix reviews each qualifying pull request in an isolated sandbox and posts a real GitHub Review, inline on the lines at fault, with a Checks status on the pull request.
How it works
From install to inline comments
- 01
Install the GitHub App
Install it on your account or organization, then pick the repositories to track. Nothing else is visible to Vulnix.
- 02
A pull request opens
Vulnix scans what actually changed, in a fresh isolated sandbox, with the same engine as a full pentest.
- 03
The review lands on GitHub
A real GitHub Review with inline comments on the lines at fault, and a Checks status on the pull request.
Included on every plan
Reviews a month, without touching your pentests
- PR reviews a month on Free
- 5
- on Builder
- 20
- on Startup
- 50
- on Pro
- 200
Policy per repository
Decide how strict each repository is
Every tracked repository has its own policy over your organization's defaults, so a payments service can block merges while an internal tool only comments.
- Automatic review on or off
- Block the merge on findings (Pro)
- Re-review when new commits are pushed
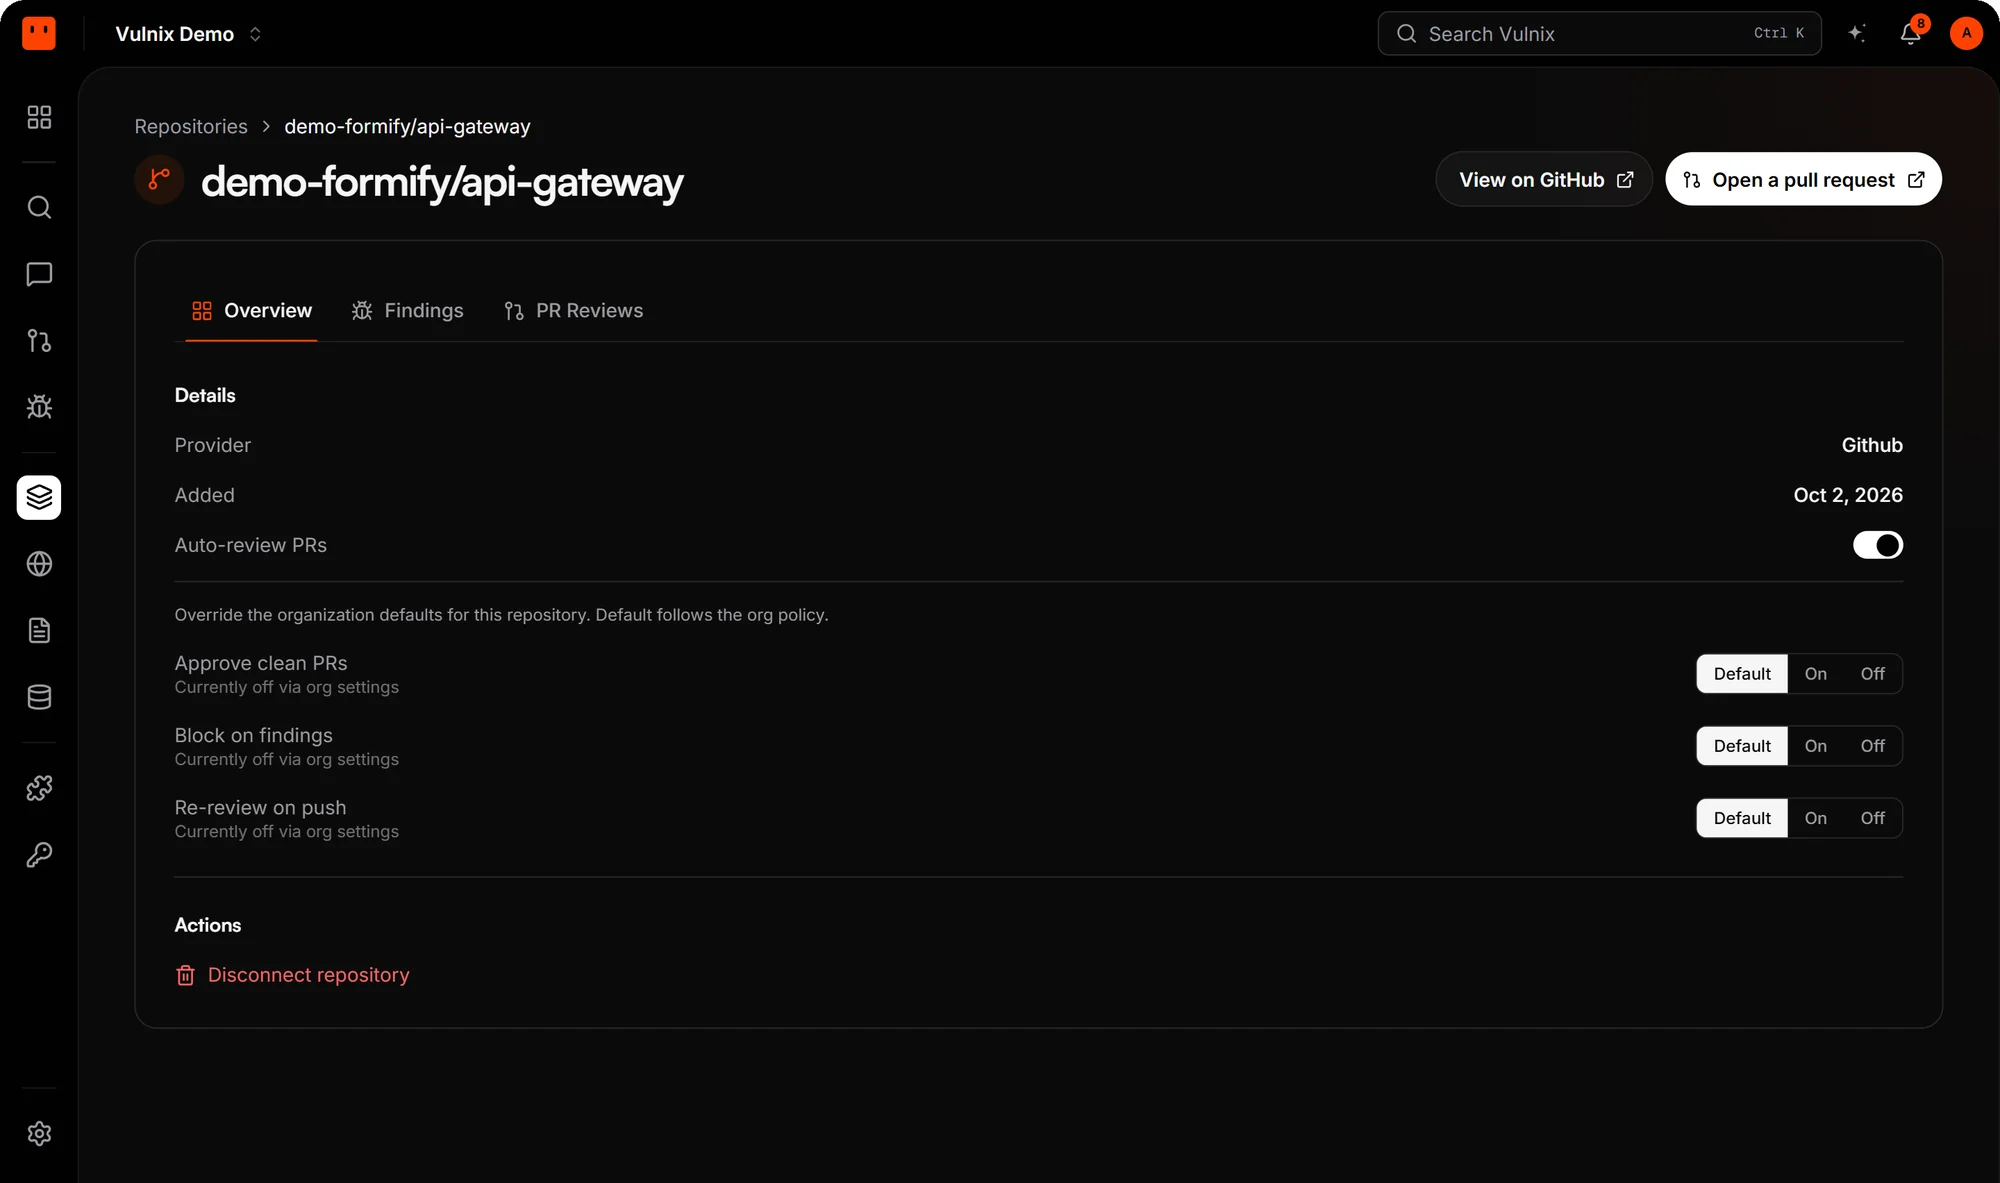
Three switches, per repository
Review automatically
Turn automatic review on or off per repository, layered over your organization's defaults.
Block the merge
On Pro, the Checks status fails when a review finds issues, so nothing ships past your branch protection.
Re-review on push
Push new commits to a reviewed pull request and it is reviewed again, or keep the first verdict.
Why it matters
Security in the review, not after the release
Where developers already are
Comments on the diff, in GitHub, on the line that needs to change. No new tool to open.
Before it ships, not after
A vulnerability caught in review never reaches production, and never needs a pentest to find it.
Scoped to the change
A diff-scoped review of what the pull request touches, so the verdict is about this change.