Another user's invoice
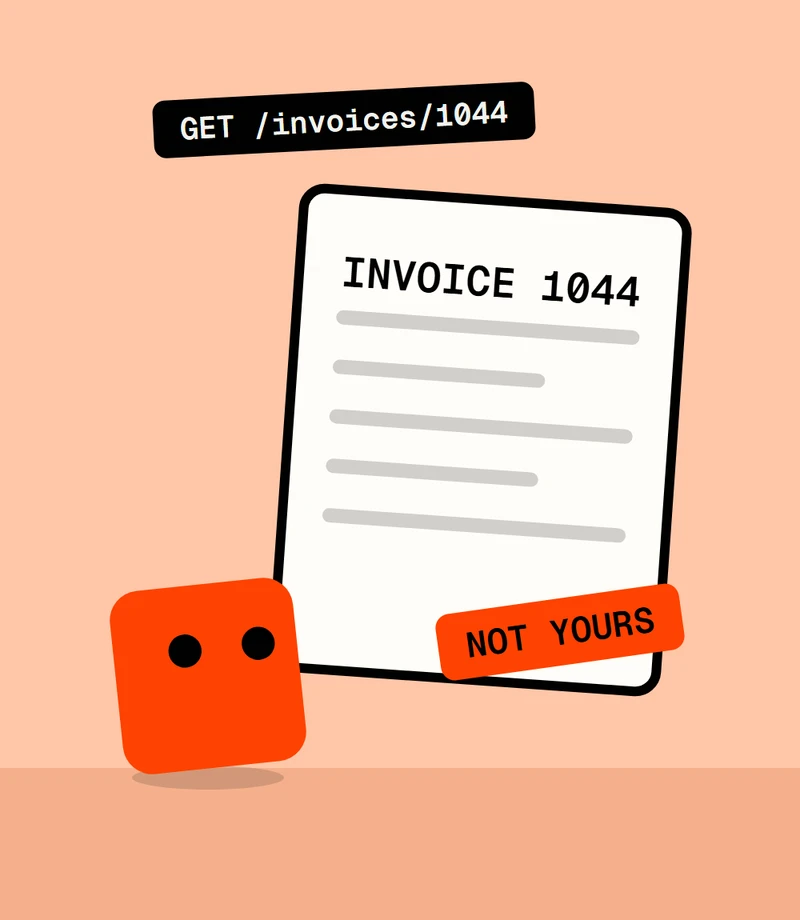
Signed in as one test account, it asks for invoice 1044. A second account confirms the invoice belongs to someone else. Both requests come with the finding.
First day on Intigriti: our agent harness found and proved a remote code execution bug, paid €3,000.
Read the story
We help every team ship securely. Just as a pentester chains one finding into the next, the agent works out the next best attack and proves it.
People combine blackbox, whitebox, PR reviews and Validate-Fix in more ways than we planned for.
Security teams use AI, automation and proof to remove the manual bottlenecks between finding a weakness and closing it, testing and fixing faster than the code changes.
Vulnix is built for teams that ship every week and get a pentest once a year. Point the agent at the scope you verified and it signs in, chains requests across features, and keeps only what it can exploit.
What reaches your queue is a finding with the request that proved it, the agent’s full trace, and a fix check that replays the same exploit once you ship. These are the kinds of proof it brings back.
Signed in as one test account, it asks for invoice 1044. A second account confirms the invoice belongs to someone else. Both requests come with the finding.
Vulnix started with a gap. Teams ship every week, but most get a pentest once a year, and the scanner that runs in between reports what might be wrong without proving any of it.
So we built an agent that works the way a pentester does. It signs in, follows one finding into the next, and keeps only what it can exploit. Every finding arrives with the request that proved it, and every fix is checked by replaying the same exploit.
We believe proof should be the default in security, not the premium tier. That is why Vulnix starts free and runs as often as you ship.