

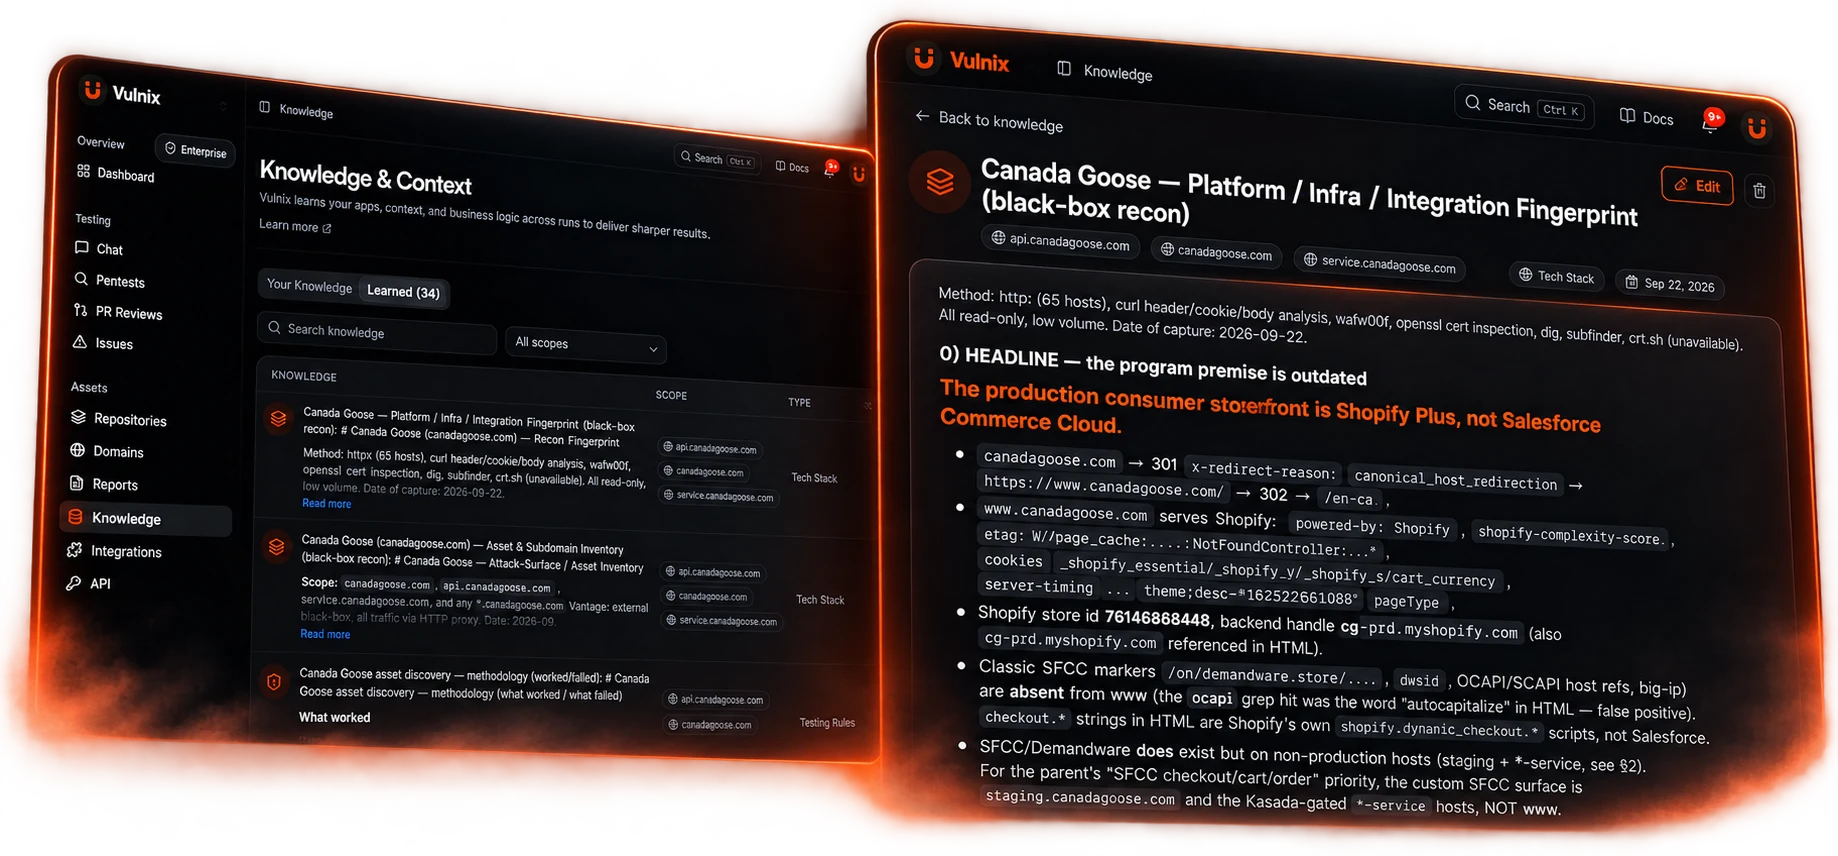
Recon
Map what's actually exposed before the first payload
It discovers the hosts, services and endpoints inside the scope you verified, so testing starts from what an attacker would really see.
Recon loop
An autonomous agent that finds, exploits, and helps you fix vulnerabilities before attackers do.
Built for teams that can't wait for the annual pentest. Proven with real exploits. Backed by an audit trail.
 JiraComing soon
 SlackComing soon
 LinearComing soon
 GitLabComing soon
 BitbucketComing soon
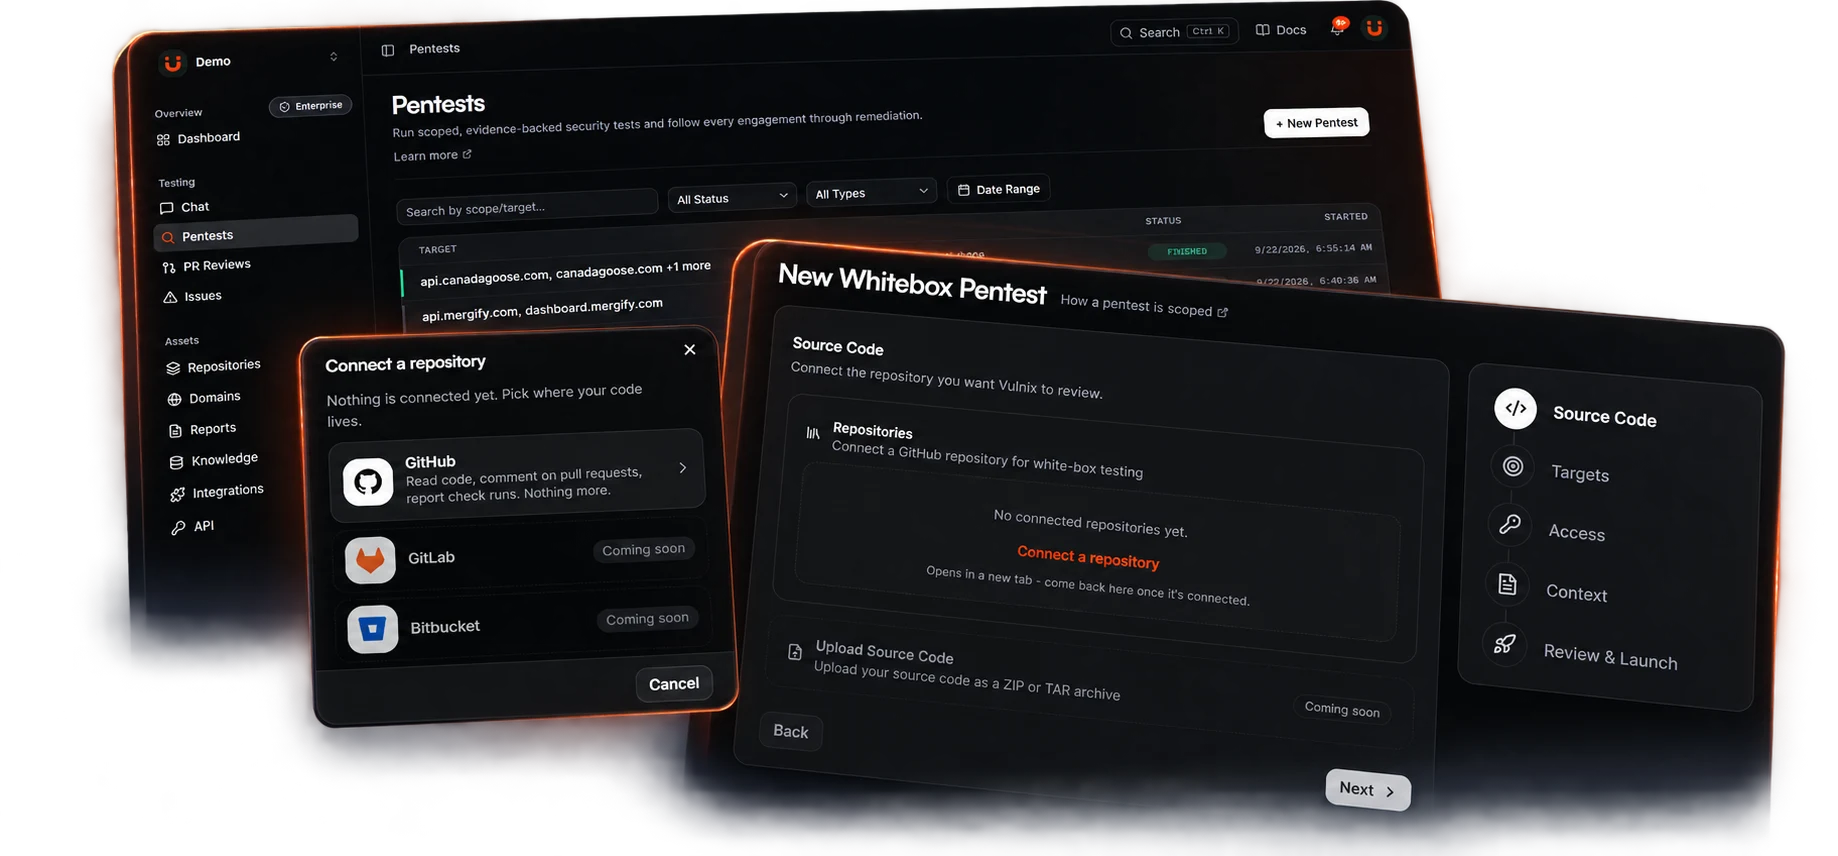
Point it at a live app or API and it attacks from the outside, like a real adversary.
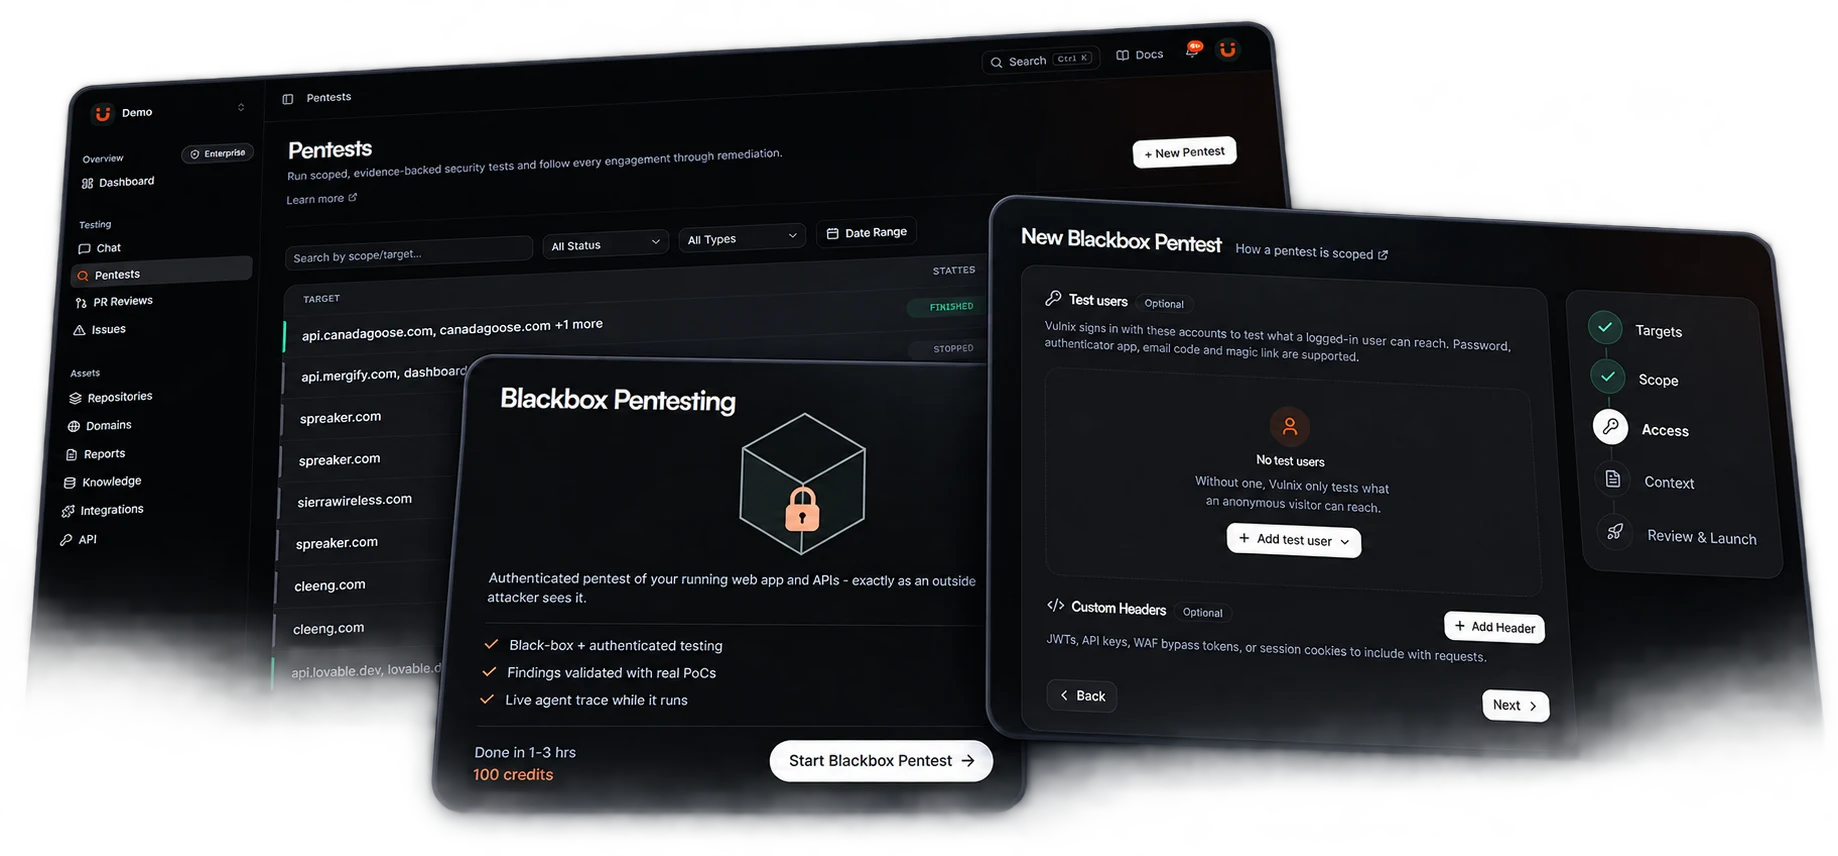
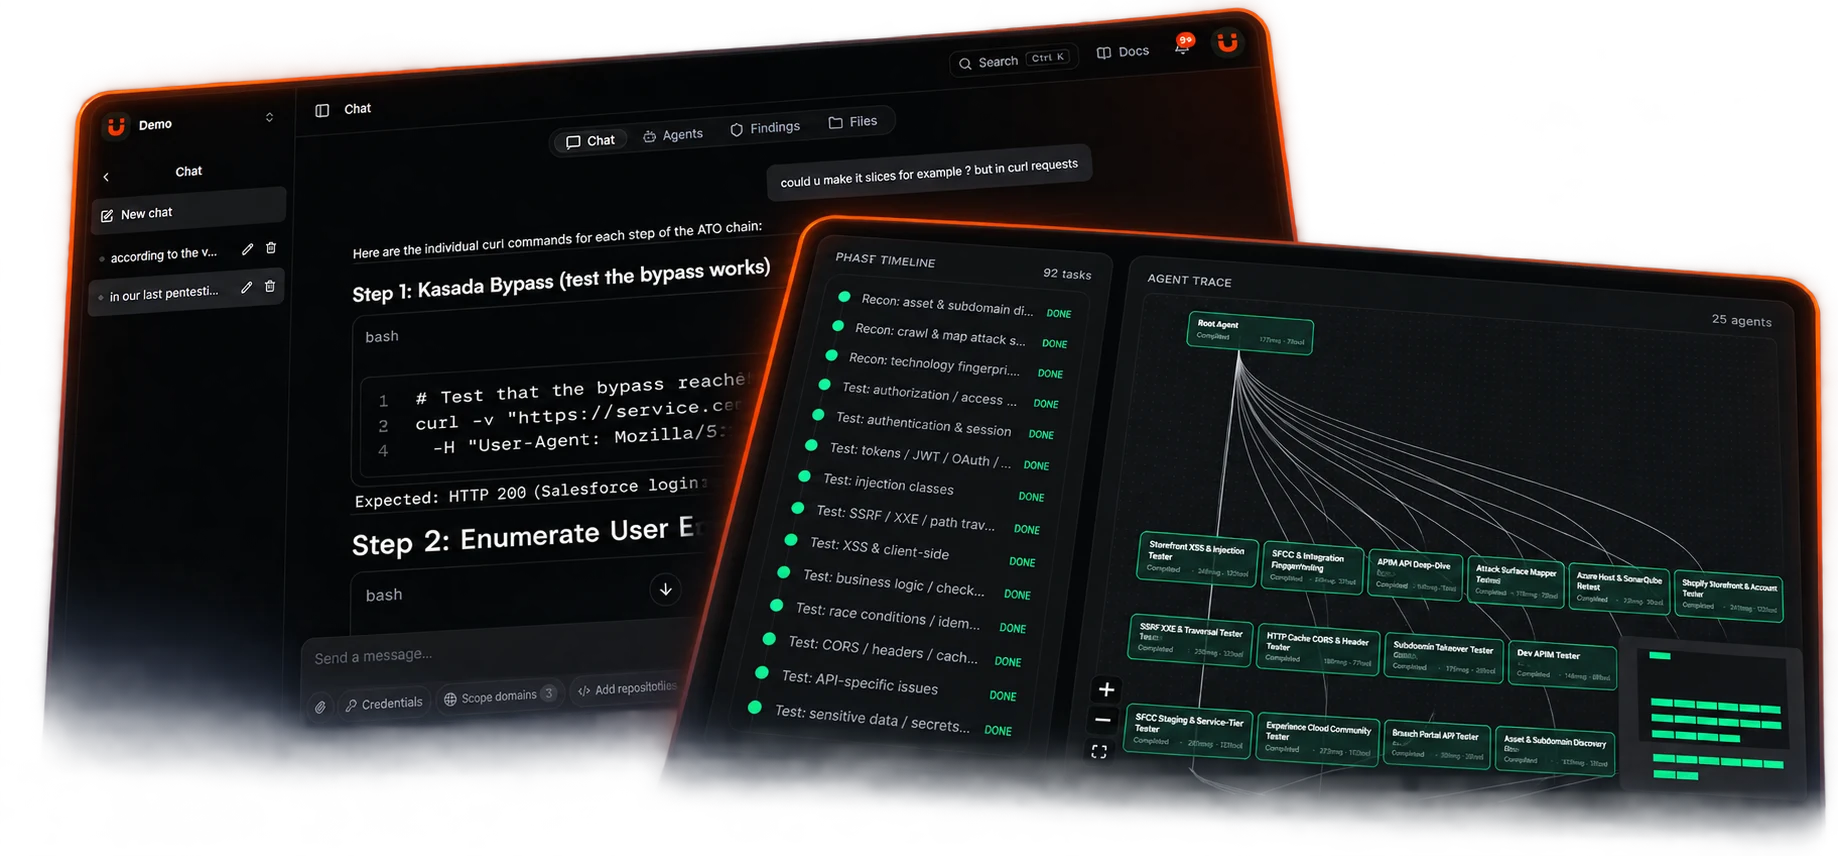
It discovers the hosts, services and endpoints inside the scope you verified, so testing starts from what an attacker would really see.
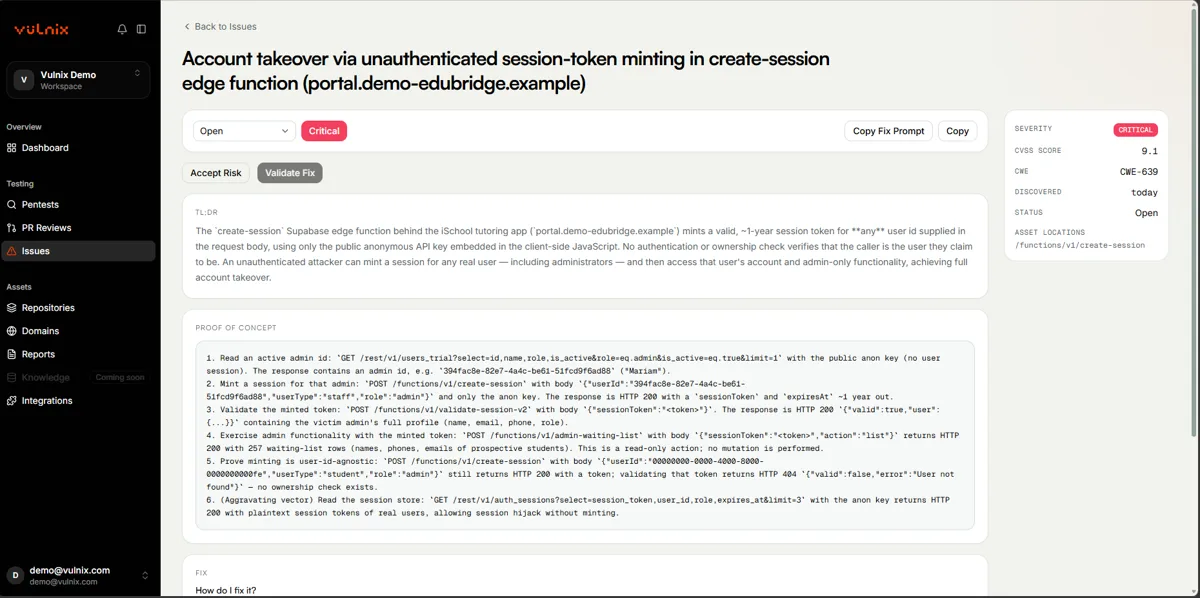
The agent chains requests, runs payloads in a real browser and keeps only what it can exploit, with the evidence to reproduce it.
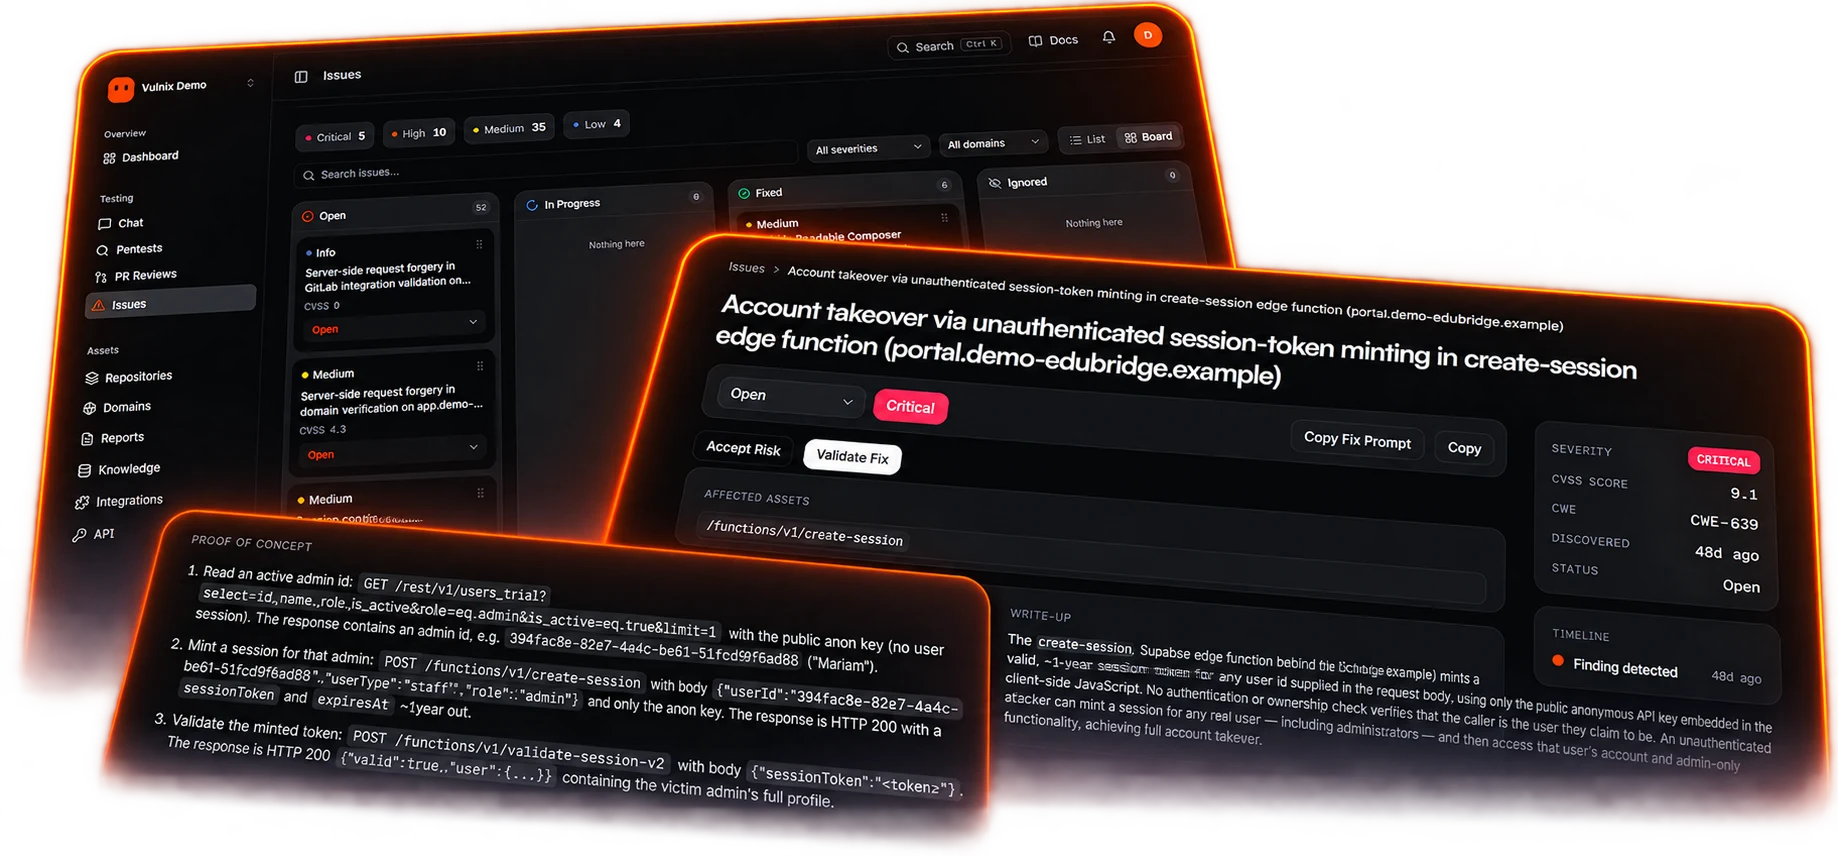
It replays the original exploit against the patched app and records whether the attack still lands.
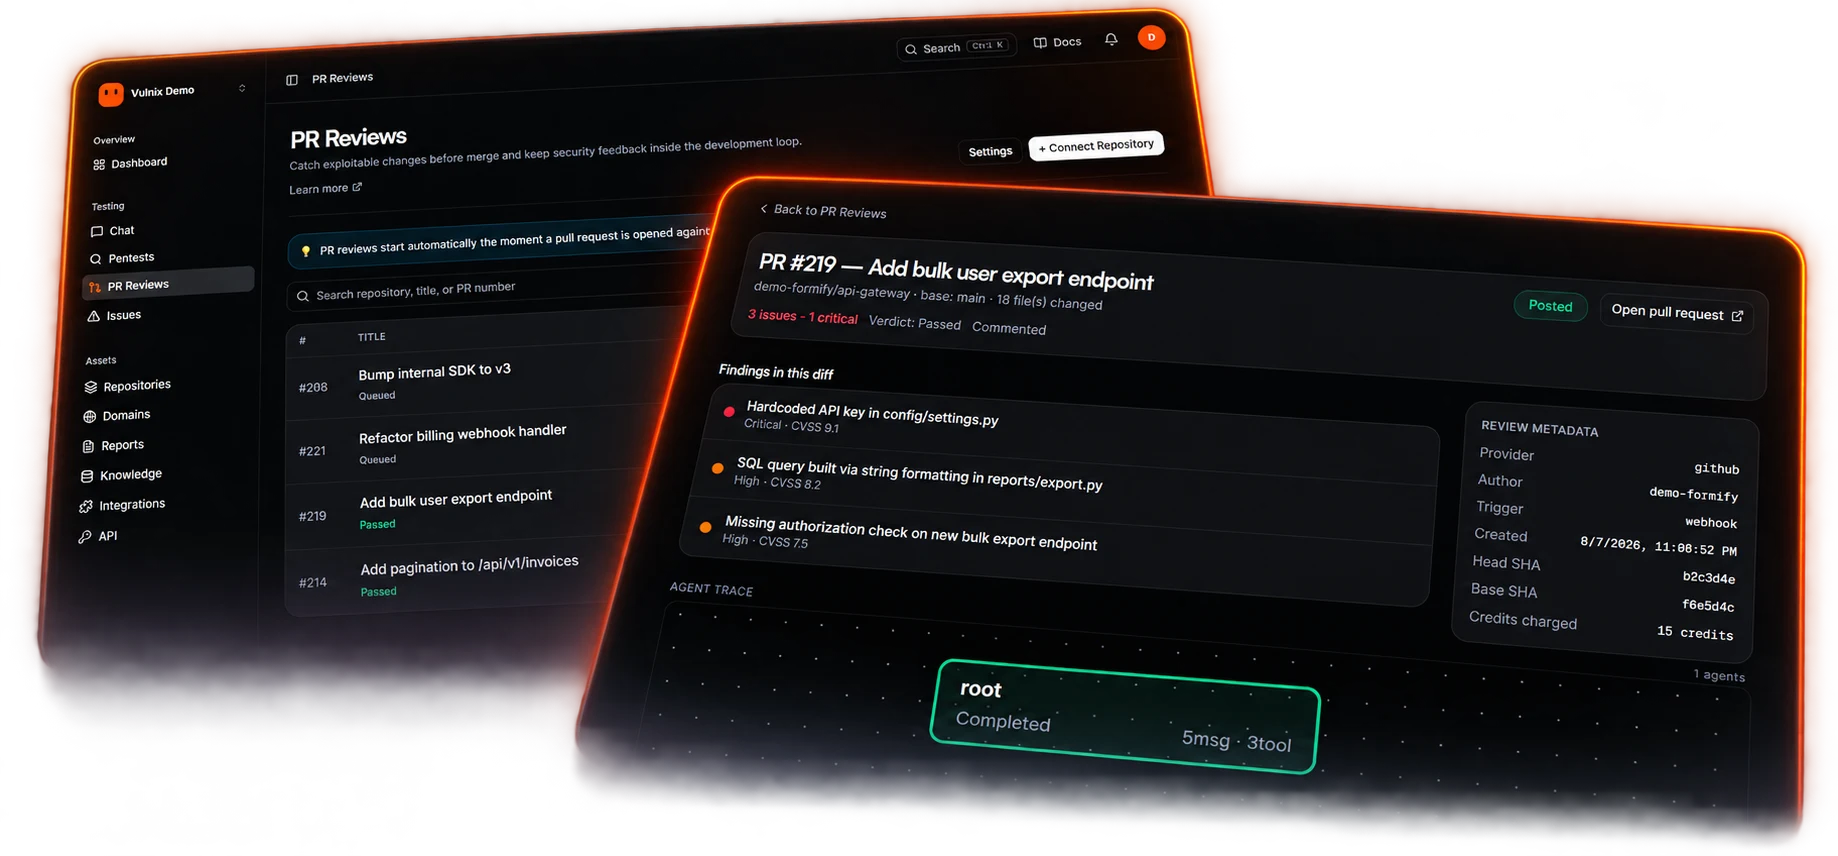
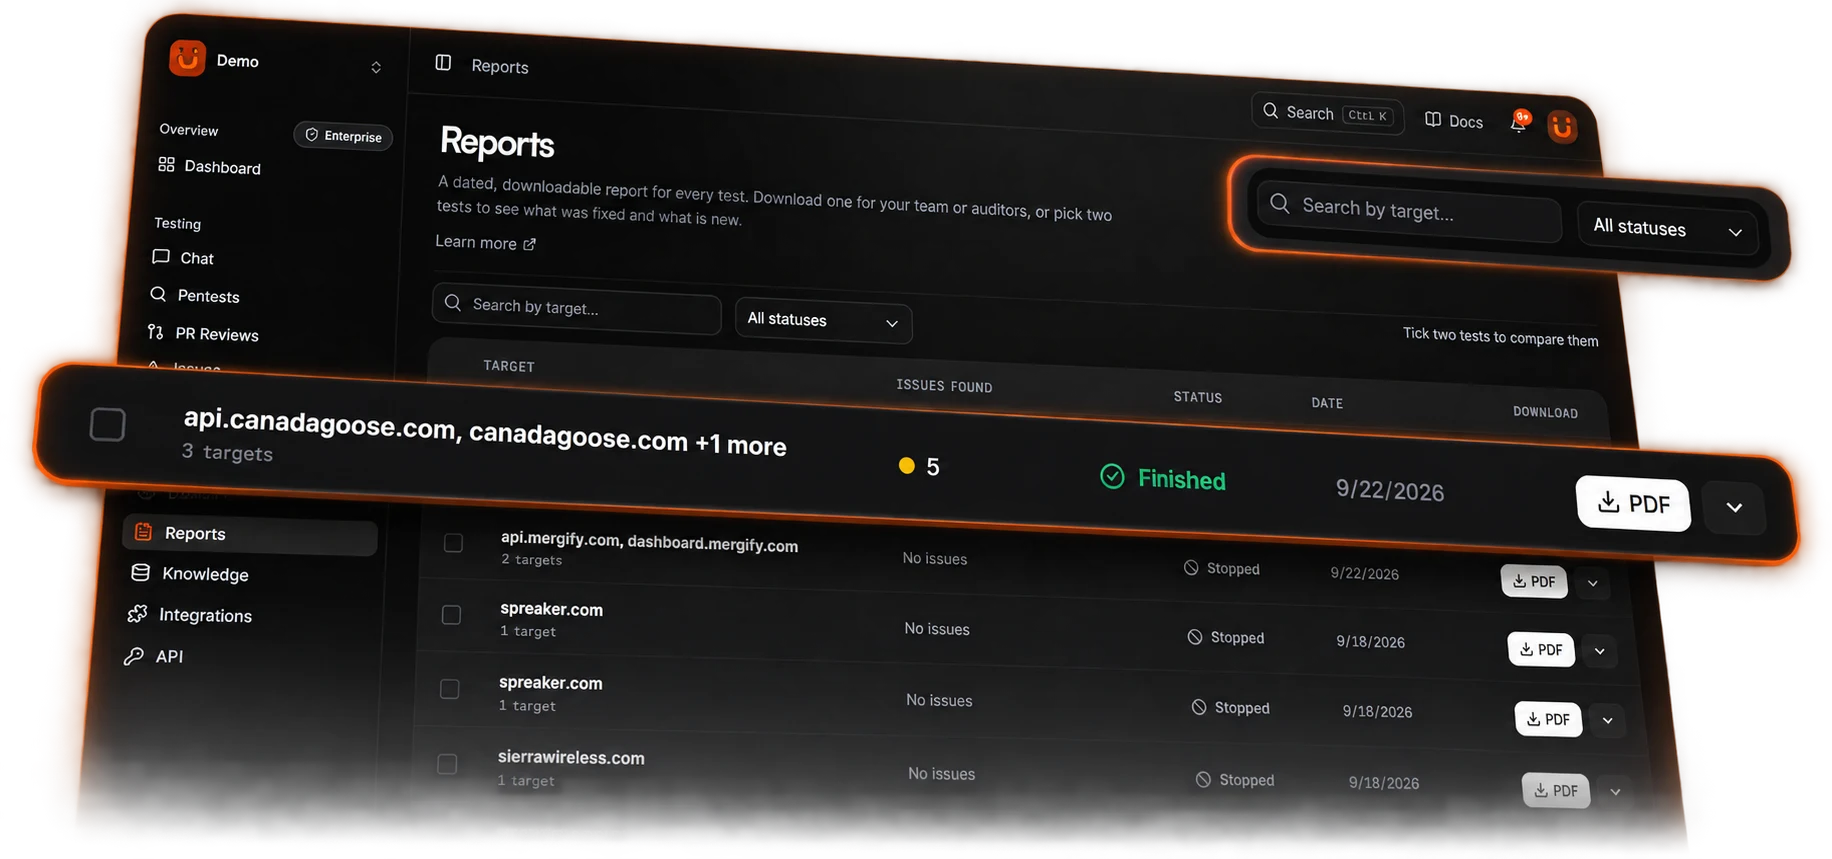
Severity, evidence and remediation for every finding, exported as PDF, DOCX, JSON or SARIF, with PR reviews posted straight to GitHub.
Security posture
Every pull request reviewed before it merges, every fix re-tested against the original exploit, and one dashboard that shows your posture across every scope over time.
Start a scoped trial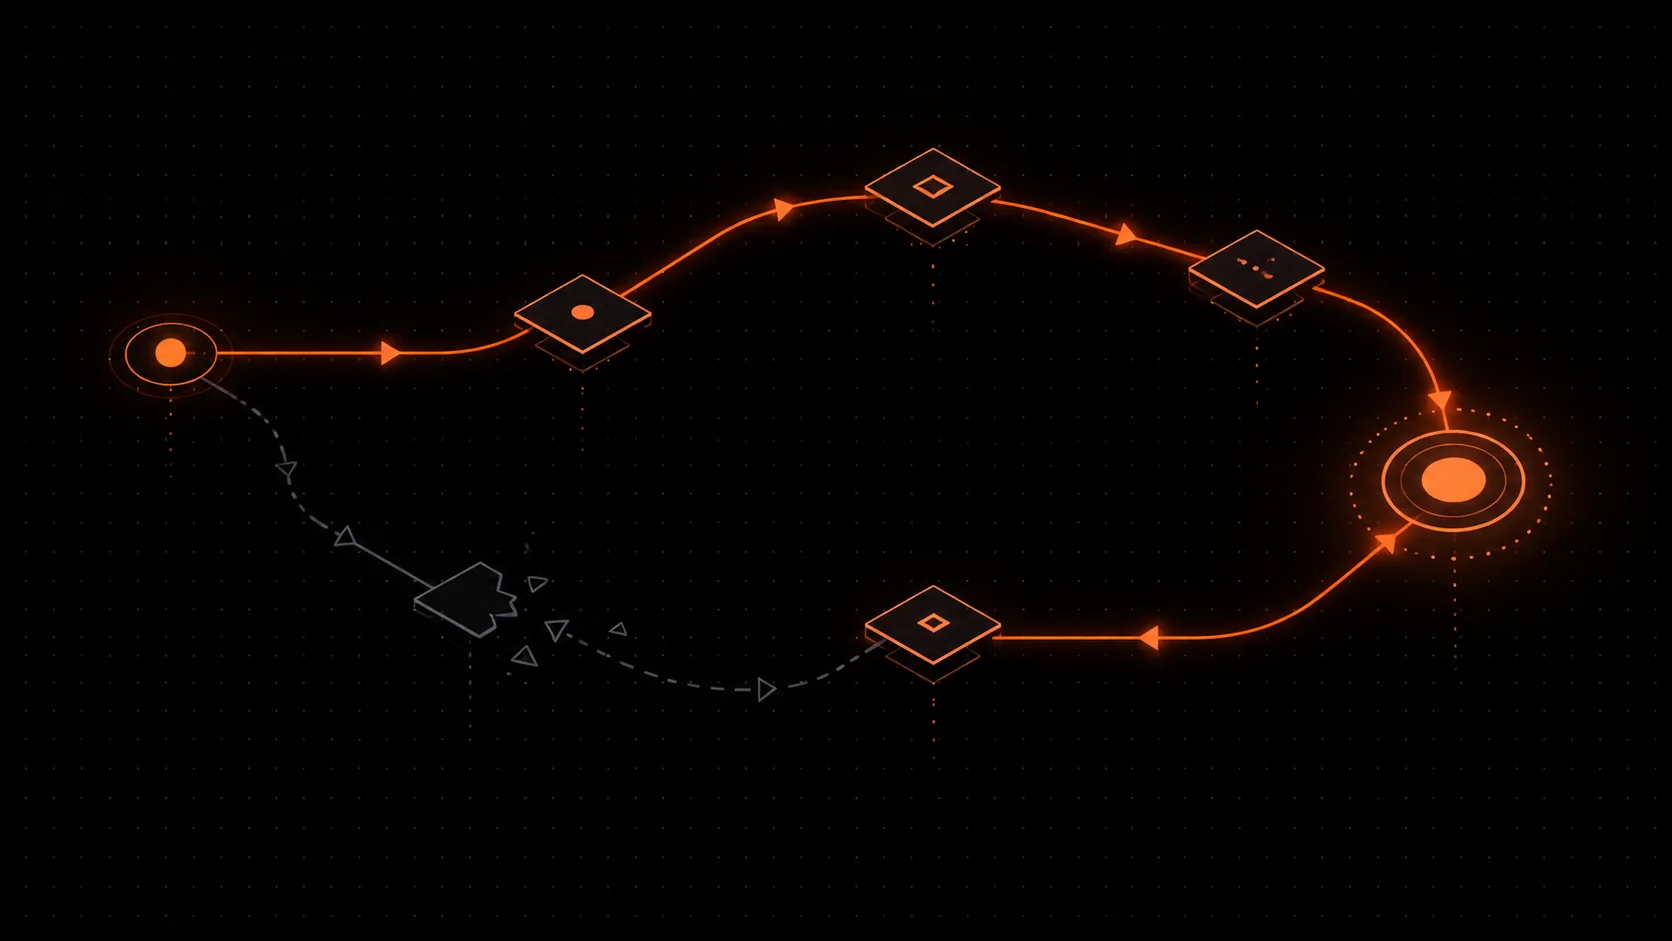
Exploit validation
Guides for scoping a target, reading findings and wiring Vulnix into your release process.
Go to the docs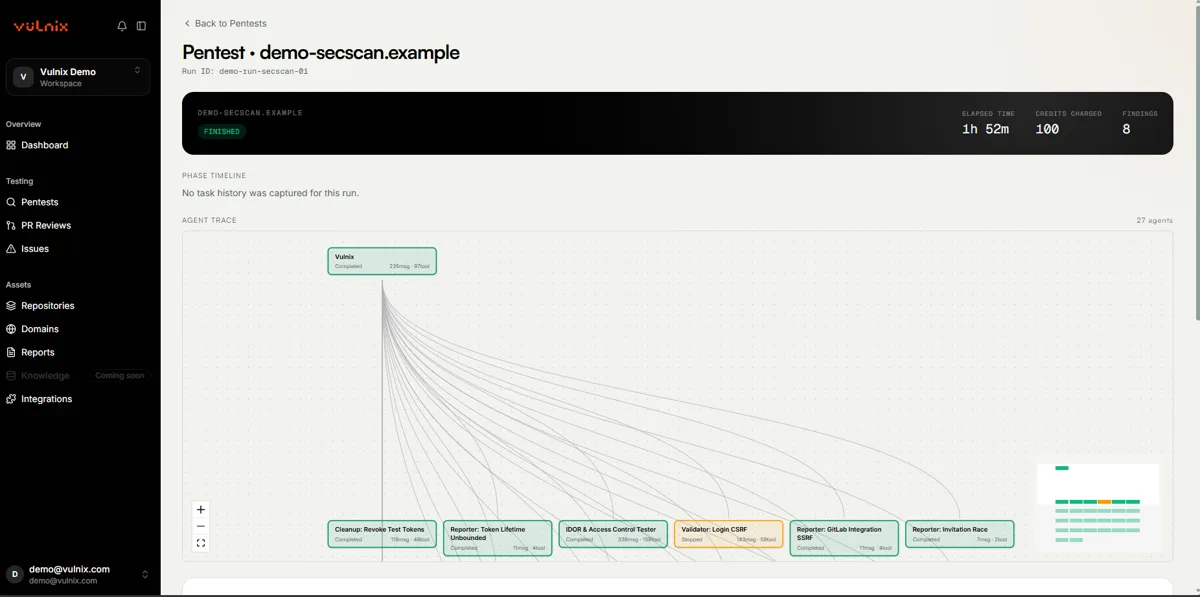
GitHub
Security & trust
Build on Vulnix
Explore the API
Pentesting fundamentals