


Findings you don't have to second-guess
Every finding carries the exploit that proved it, ranked by severity with its CWE and the steps to fix it. Every run ends in a PDF report you can hand to anyone.
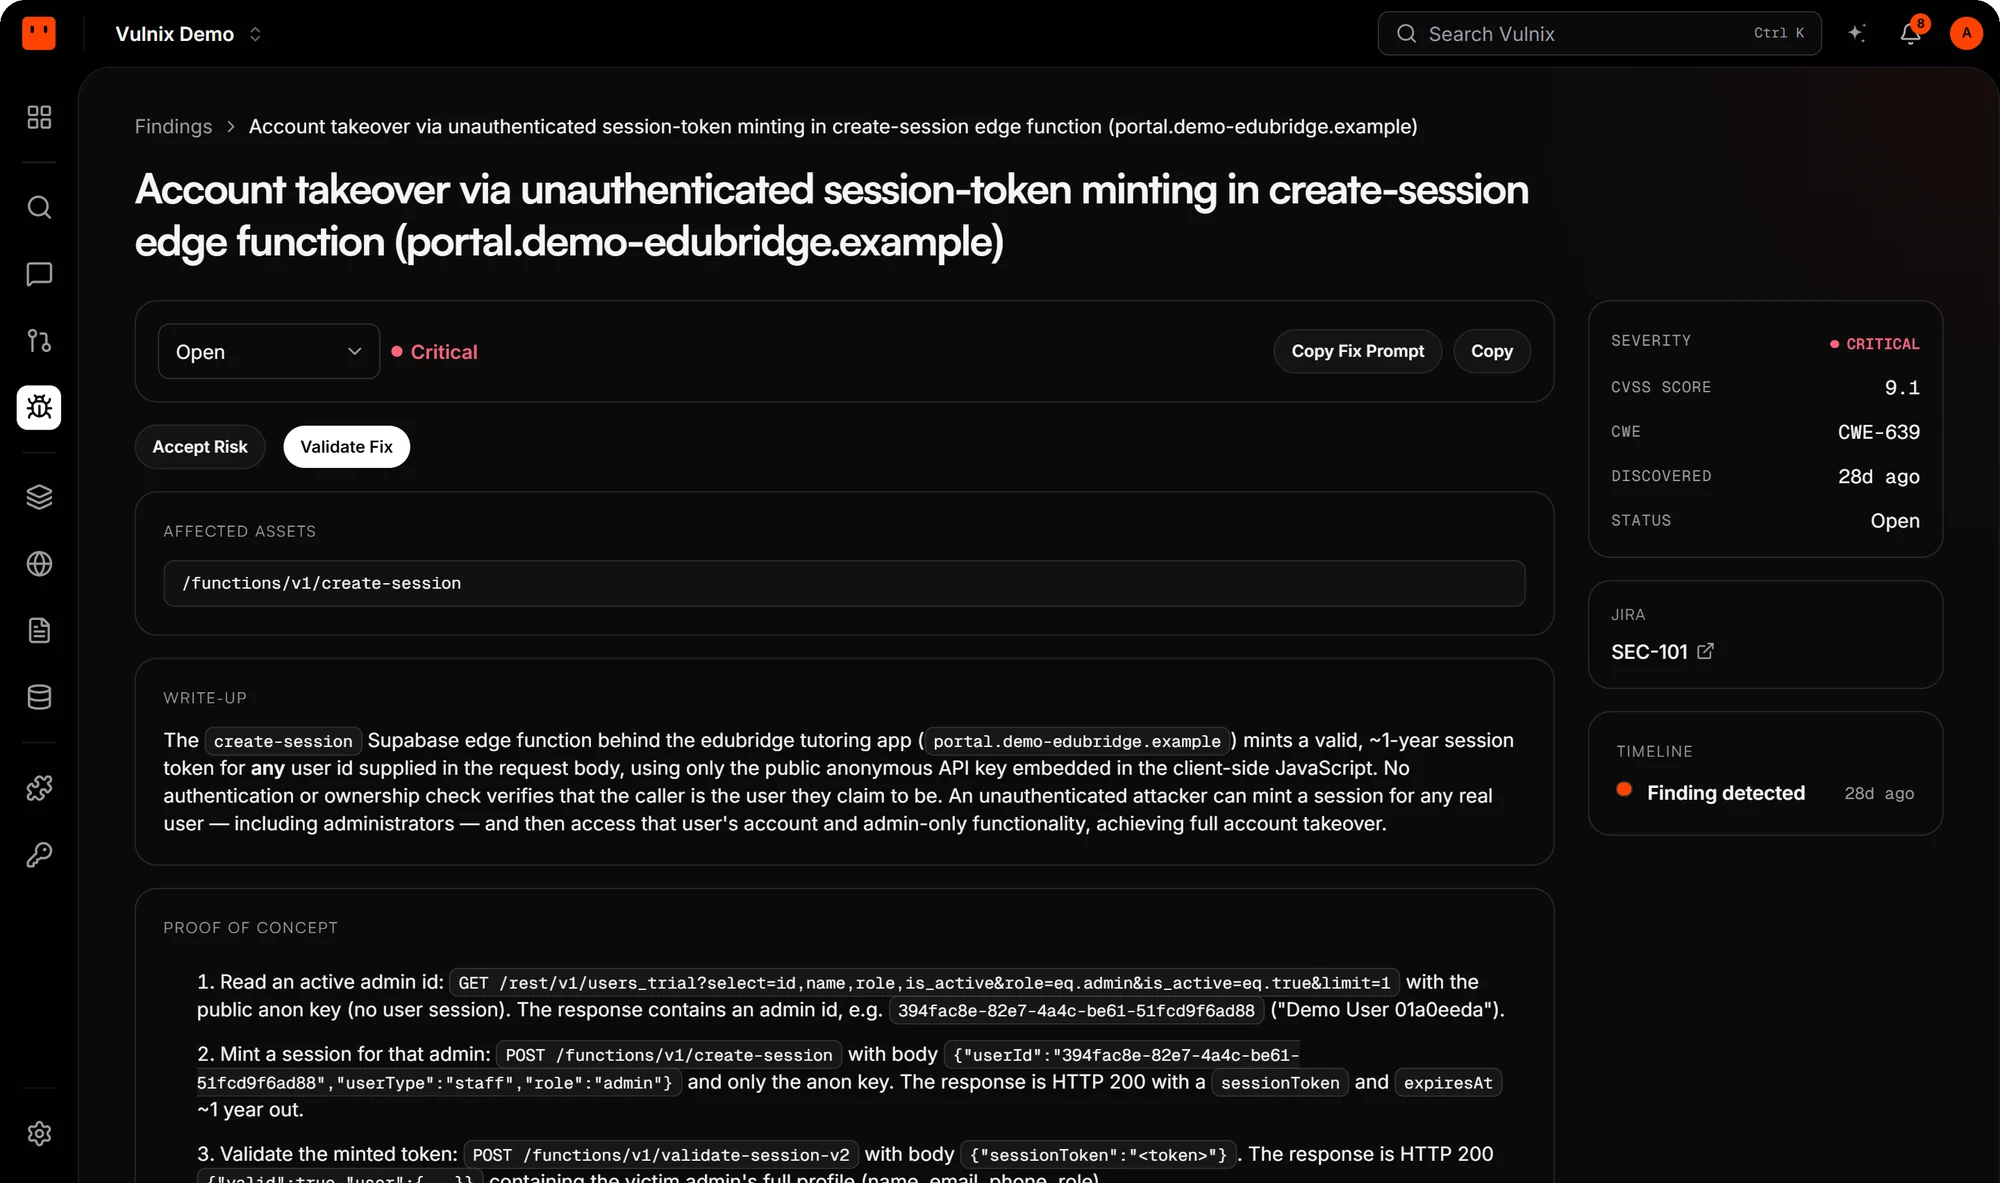

Anatomy of a finding
Everything you need to act, in one place
Severity and classification
Critical to info, with CVSS and the CWE or CVE it maps to, so it slots into how you already rank risk.
The proof
The exact request and response that reproduce a blackbox finding, or the file and line of a whitebox one.
The fix
Remediation steps for every finding, and a ready fix pull request for eligible whitebox findings.
Working a finding
From found to fixed, with a trail
- 01
Triage
Filter every finding from every run by severity, status, repository or domain, and search them.
- 02
Act on it
Mark it fixed, snooze it or accept the risk. Every change is audited: who did it, and when.
- 03
Send it on
Create a Jira issue from the finding, or open a fix pull request for a whitebox one.
- 04
Prove it's fixed
Validate Fix replays the original exploit against your patch before you close the finding.
Reports
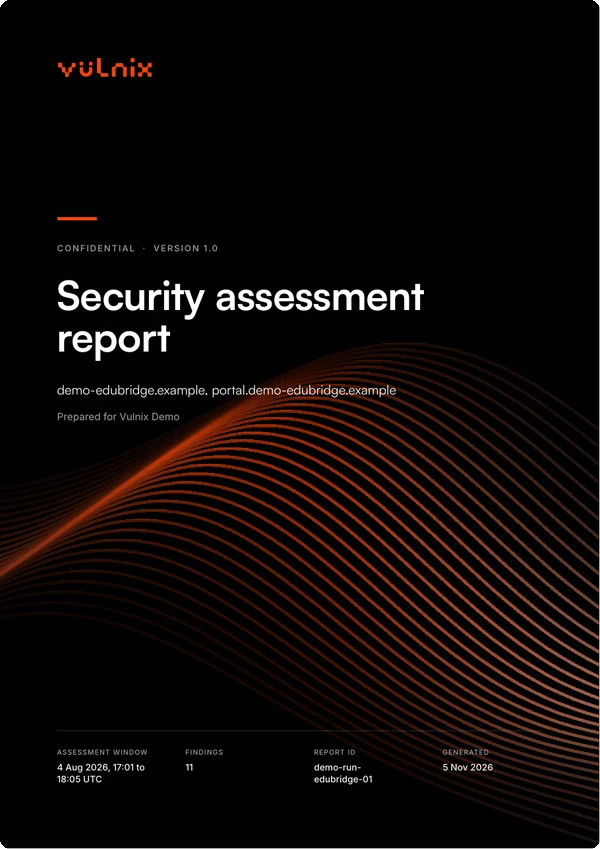
A PDF for every run
Download the report from Reports when a run ends: a shareable document with each finding, the steps to reproduce it and how to fix it.
- Findings ordered by severity, each with its evidence
- Counts and summaries computed from the run
- Compare two runs of the same scope to show progress
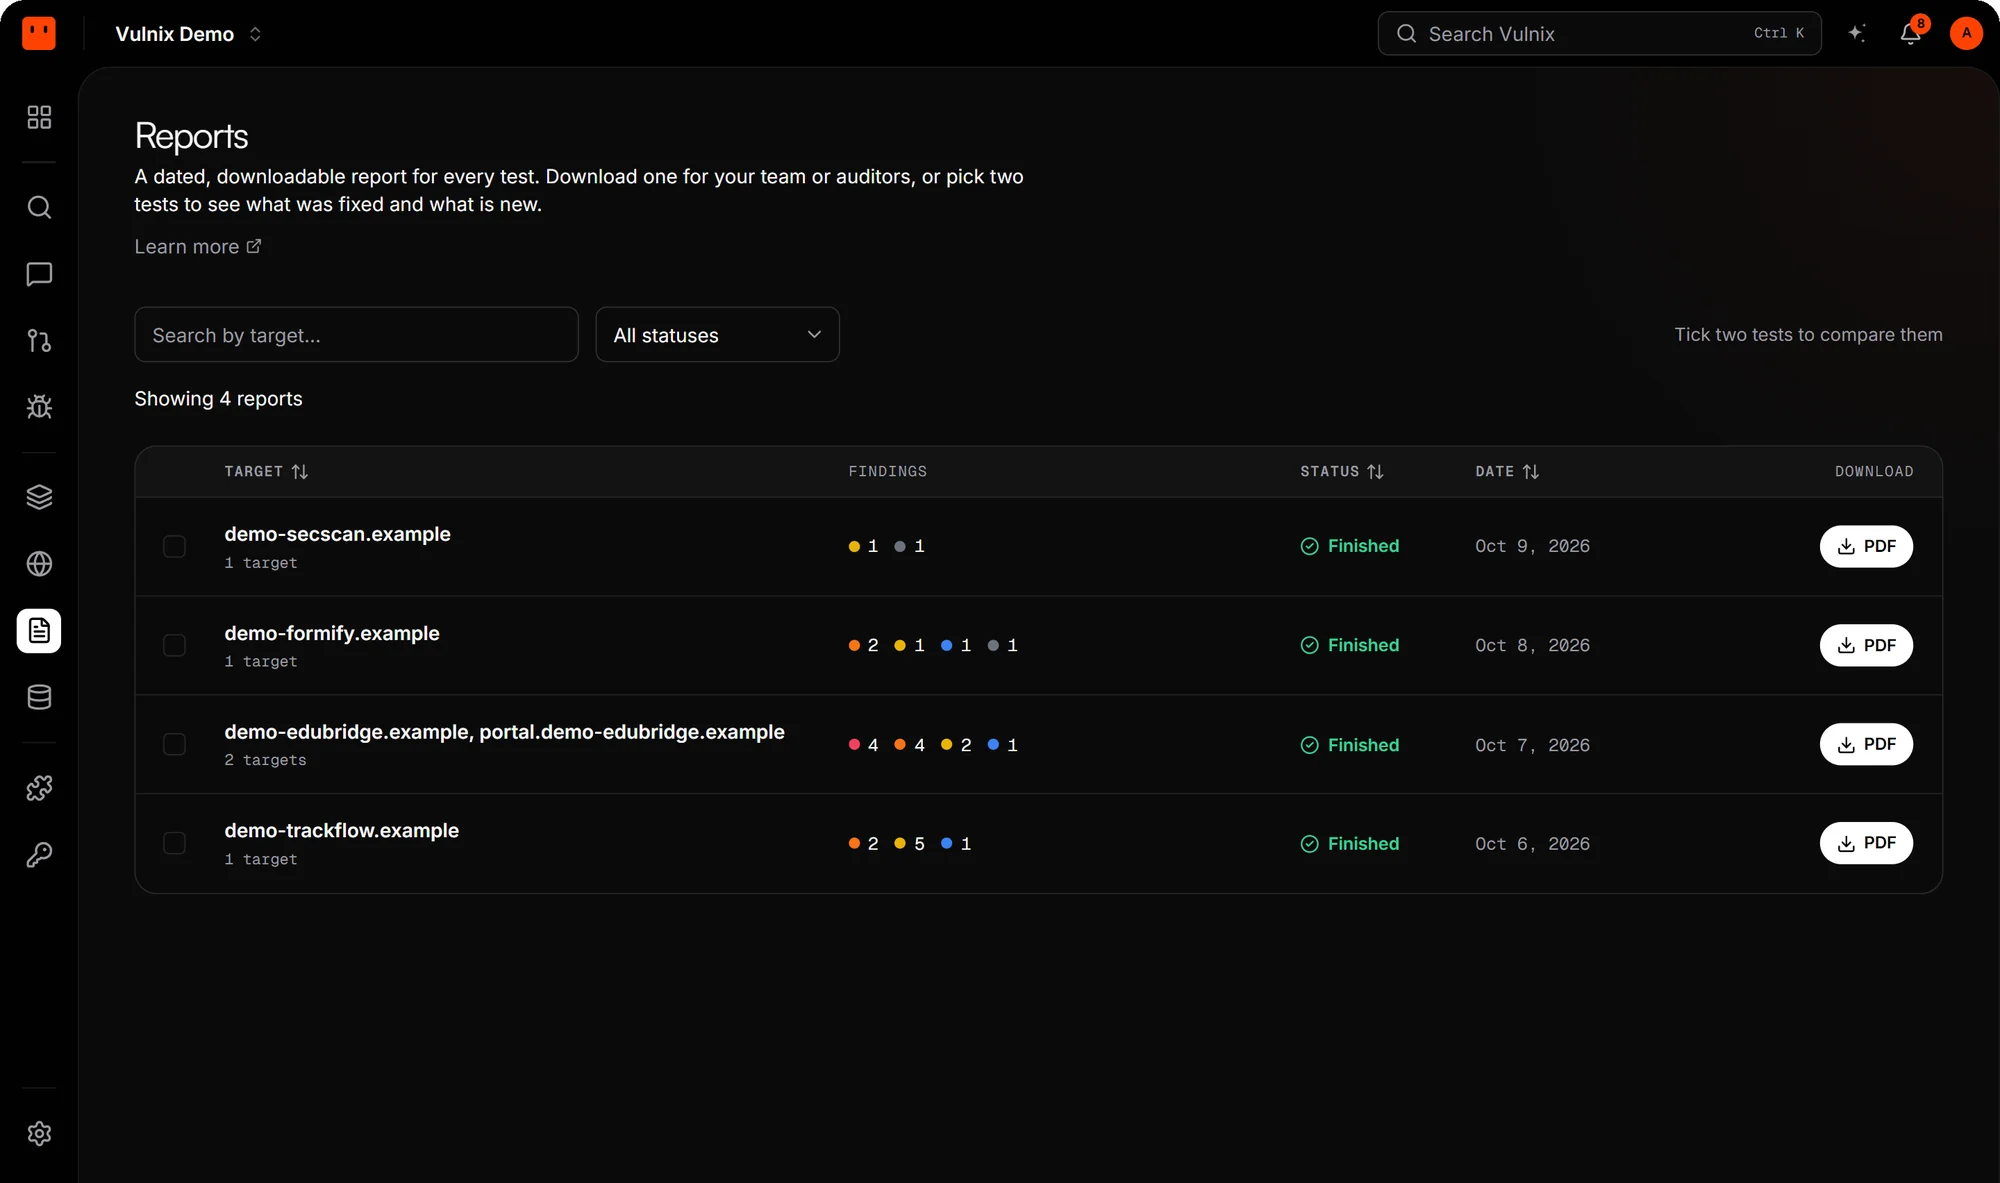
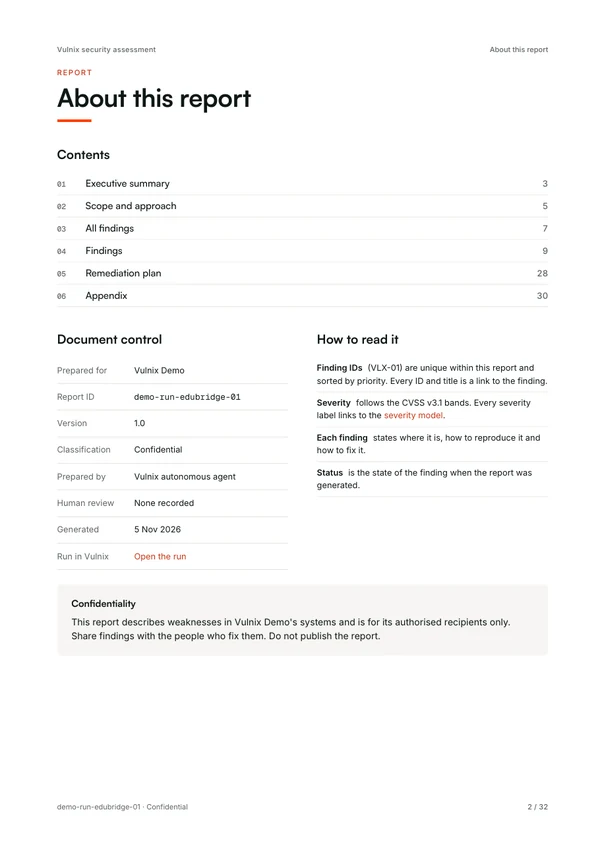
Reports that hold up
Written for people
Each finding with the steps to reproduce it and how to fix it, laid out for engineers and stakeholders alike.
Numbers you can trust
Every count and every sentence about the assessment is computed from the run, never written by a model.
Progress over time
Compare two runs of the same scope to show exactly what was fixed between them.